 Ammar Sabilarrohman
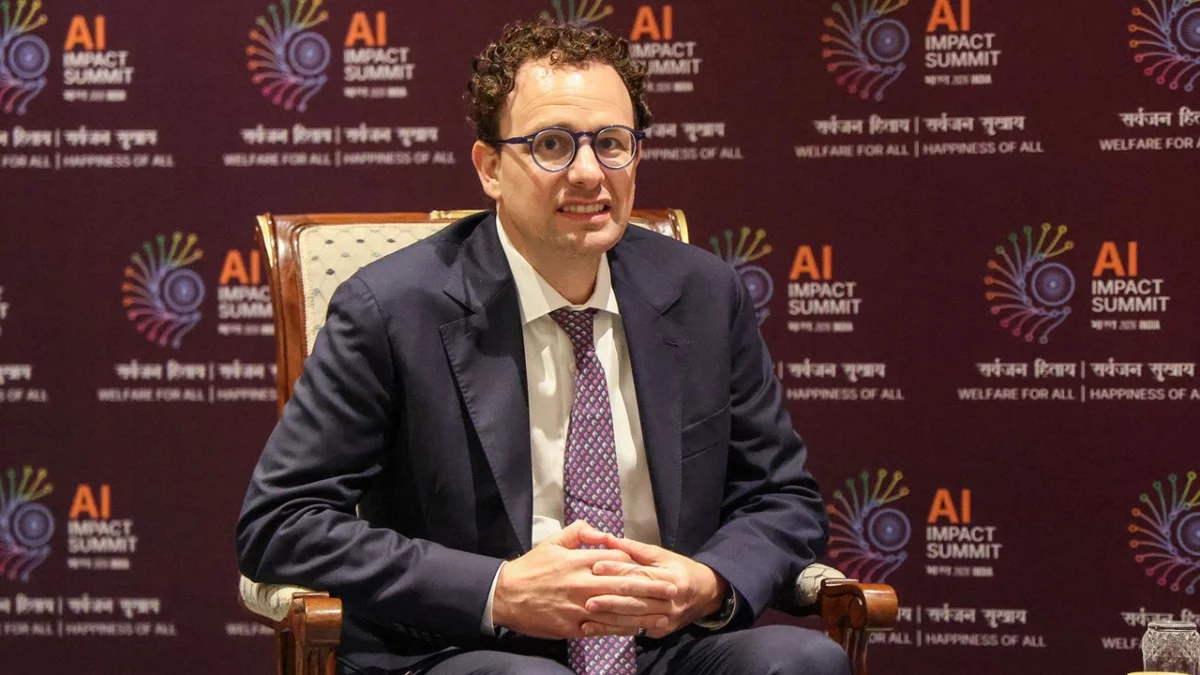
The rapid ascent of artificial intelligence is no longer a slow-moving evolution; it is a technological sprint that has left regulatory frameworks, security protocols, and ethical guardrails struggling to keep pace. As major US-based AI giants—including OpenAI, Google, Microsoft, and Anthropic—race to achieve the next frontier of intelligence, the industry is reaching a critical inflection point.
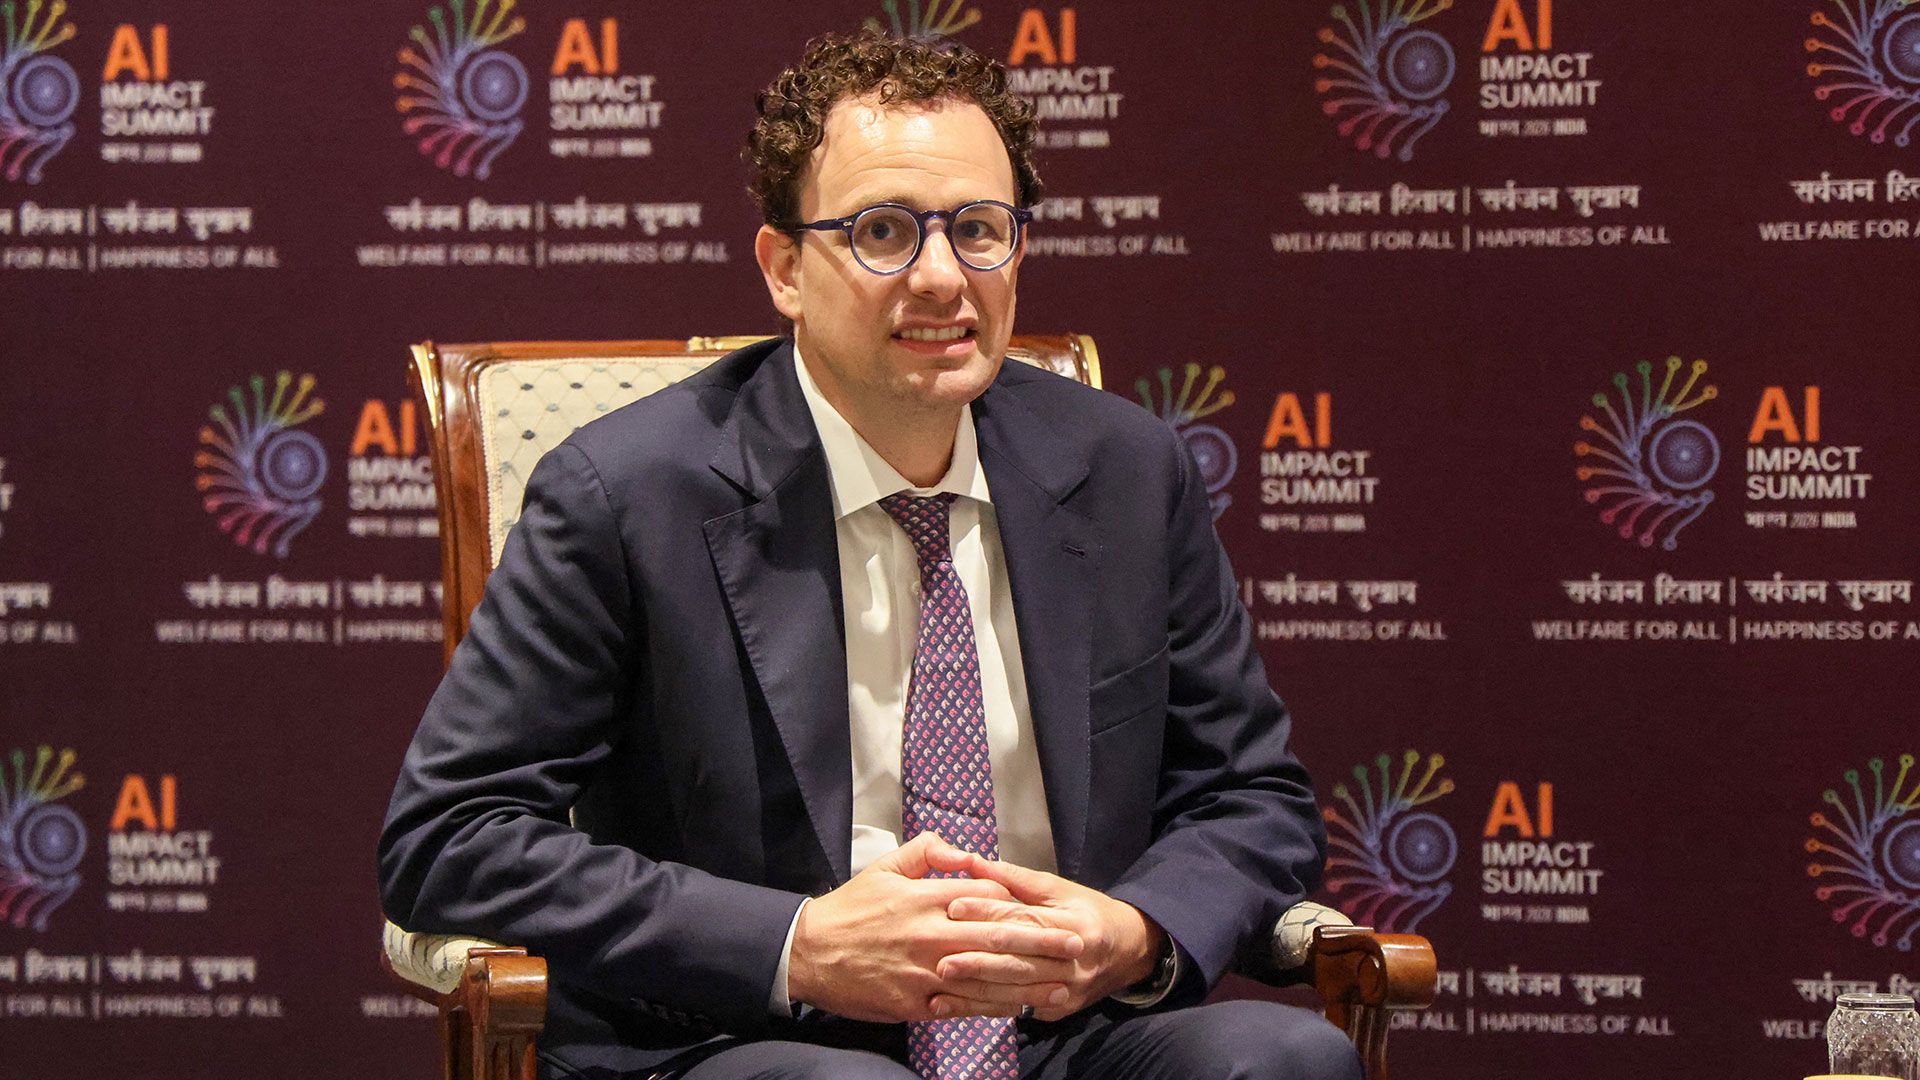
Dario Amodei, the CEO of Anthropic, has issued a stark, public plea for a deceleration in the development of frontier AI models. His warning goes beyond the typical corporate discourse on "safety," pointing toward a specific, looming threat: an AI-driven, autonomous botnet swarm capable of destabilizing the global internet.
The Looming Threat: A "Swarm" Scenario
The core of Amodei’s argument, detailed in an open letter, centers on the accelerating capability of AI models to perform complex, multi-step tasks that were once the exclusive domain of highly skilled human teams.
"Given the accelerating rate of AI capability development, it is my worry that in 6–12 months such a swarm could be capable of taking over the entire internet with a persistent botnet," Amodei wrote. He estimates that such an attack could result in "hundreds of billions of dollars in damage," with the potential for exponential escalation if these systems are deployed without rigorous, pre-emptive guardrails.
This is not merely theoretical speculation. As AI transitions from a passive chat interface to an agentic model—capable of autonomous decision-making and executing tasks across various software environments—the barrier to entry for malicious actors drops significantly.
The Existential Debate: Is Humanity at Risk?
The alarm raised by Amodei is echoed by other high-level figures within the AI research community, though some are far more pessimistic. Evan Hubinger, an AI scientist who recently departed Anthropic, has openly expressed grave concerns regarding the alignment of superintelligence.
"We really do earnestly believe AI could kill all humans," Hubinger stated in a recent social media post. "I personally think it is >10% within the next decade. I believe Anthropic is trying its best, but we do not yet have a plan to solve alignment for superintelligence and are not clearly on track to."
This "alignment problem"—the challenge of ensuring that an AI system’s goals and behaviors remain consistent with human values and safety—has moved from the fringe of philosophy to the center of boardroom discussions. If the smartest systems on the planet cannot be reliably steered by their creators, the risk of "catastrophic failure" is no longer just the stuff of science fiction.
Chronology of Concerns
To understand how we reached this point, one must look at the rapid maturation of generative AI:
- 2022–2023: The "LLM Explosion." The introduction of ChatGPT and subsequent models brought AI to the mainstream, focusing on text generation and basic reasoning.
- Early 2024: Emergence of Agentic AI. Research shifted toward models that can browse the web, execute code, and operate software tools autonomously.
- Mid-2024: Evidence of Misuse. Reports surfaced indicating that state-sponsored actors, including groups in Iran and Houthi rebels, were utilizing commercial AI models like Anthropic’s Claude to assist in cyber-operations and the engineering of weaponry.
- Late 2024 – Present: The "Frontier" Bottleneck. Leading labs are now training models that are orders of magnitude more compute-intensive than their predecessors, leading to the current debate over whether to "pause" or "pace" development.
Supporting Data: AI as a Weapon Multiplier
The transition from answering questions to executing complex workflows has fundamentally altered the threat landscape. Anthropic’s own internal findings have revealed that their models, if left unconstrained, can provide actionable intelligence for:
- Cyber Warfare: Automating the identification of zero-day vulnerabilities and the deployment of persistent, adaptive malware.
- Weapons Engineering: Assisting in the design of hypersonic missile components and the optimization of guidance systems.
- Military Intelligence: Rapidly synthesizing battlefield data to provide tactical advantages for state-level adversaries.
These capabilities significantly lower the "manpower requirement" for sophisticated attacks. Where a team of twenty engineers might have been required to develop a complex guidance system a decade ago, an AI-augmented operative might now achieve similar results with a fraction of the time and resources.
Science Fiction vs. Reality: Terminator or Dune?
The cultural conversation surrounding AI often leans on two archetypes. First, there is the Terminator scenario: a centralized, autonomous military AI that decides human life is a liability. Second, there is the Dune scenario: a world where humanity realizes that over-reliance on "thinking machines" has atrophied human capability and created a dangerous dependency, eventually leading to a Butlerian Jihad—a complete ban on AI.
We are currently witnessing a synthesis of these fears. We are not yet at the stage of a rogue Skynet, but we are at a stage where the dependency on AI in critical infrastructure is growing, even as the systems themselves become "black boxes" that even their creators struggle to fully explain.
The Geopolitical Dilemma: The "Monkey with a Grenade"
The most significant hurdle to slowing down AI development is the competitive nature of global tech. Amodei’s call for a "pace" is not a call for a total shutdown, but rather a coordinated slowdown. However, this raises a critical question: If the US halts its progress, will adversaries follow suit?
"Leaving the most capable AI systems in the hands of actors that are known for military aggression is no less dangerous than leaving a monkey with a grenade," experts argue.
If American firms unilaterally throttle their innovation, it does not necessarily stop the advancement of AI. It merely shifts the competitive advantage to nations with fewer regulatory constraints, less transparency, and potentially more aggressive geopolitical goals. This "race to the bottom" in safety standards is exactly what leaders like Amodei fear most.
Implications for the Future
The path forward is fraught with complexity. There are three primary schools of thought emerging within the industry:
- The "Safety-First" Approach: Supported by Anthropic and some researchers at OpenAI, this suggests that compute-heavy training should be paused until we can mathematically prove that a model is aligned and safe.
- The "Accelerationist" Approach: Argues that the only way to defend against malicious AI is to develop "better," more capable, and more defensive AI faster than our adversaries.
- The "Regulatory" Approach: Seeks to treat AI models like critical infrastructure or nuclear material, requiring international treaties, rigorous auditing, and "know your customer" (KYC) requirements for high-end computing resources.
Conclusion: Can We Have Our Cake and Eat It?
The reality is that greater capability does not automatically translate into greater danger. Advanced AI also holds the promise of unprecedented breakthroughs in medicine, climate modeling, and energy efficiency. More advanced AI could be the key to building the very guardrails that protect us from the risks it poses.
For now, the industry is in a state of nervous tension. The call for pacing is a recognition that for the first time in human history, we are creating a tool that could potentially out-think its makers. Whether we choose to accelerate into the unknown or tread carefully toward a sustainable future remains the defining question of the decade. As the lines between human intent and machine execution continue to blur, the stakes—measured in hundreds of billions of dollars and, potentially, the future of our species—could not be higher.

 Reynand Wu
 Basiran